latest writeups
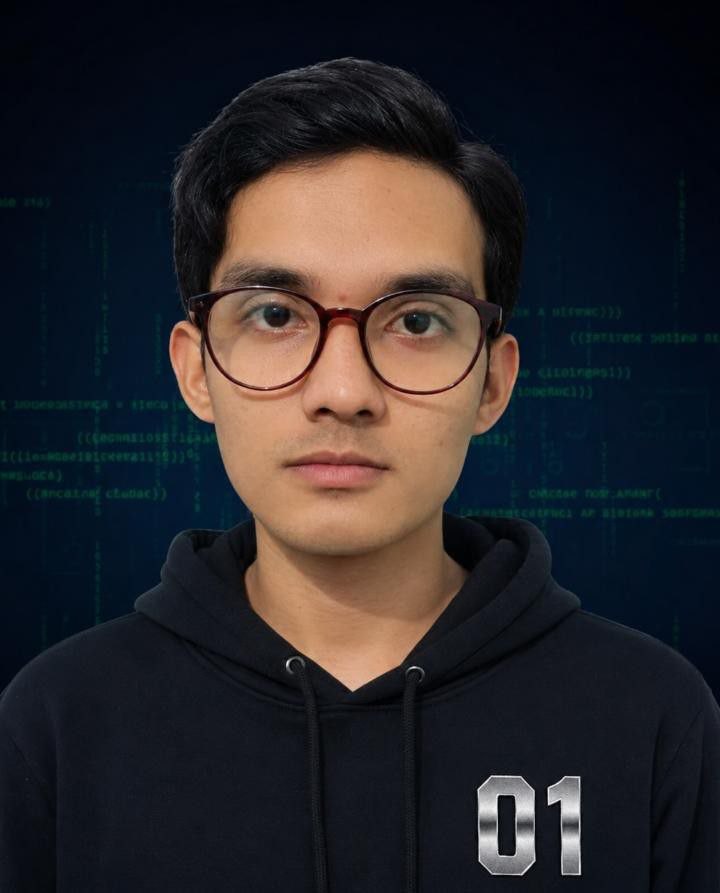
about me
👾 Hey there! I’m Rifat Al Jubayer, an independent cybersecurity professional with an insatiable curiosity for how things work, especially when it comes to technology. What started as a fascination with programming languages quickly evolved into a deep passion for both software development and cybersecurity. I thrive on understanding how technology can solve real-world problems while ensuring everything stays secure.
career experience
Over the years, I’ve discovered and exploited over 300 security vulnerabilities across more than 70 web applications, working with major names like Apple and Microsoft. Each vulnerability I uncover is a chance to learn something new and sharpen my skills—it’s what keeps me motivated and always looking for ways to push the limits of what’s possible in cybersecurity.
I’m constantly exploring new areas of tech and picking up new skills along the way. Whether it’s diving deeper into security or building something from scratch, I’m always excited to keep learning and contribute to a safer, smarter digital world.
connect
View my CVblog
projects
cv
published cves
- CVE-2026-61835 — Directus SSRF protection bypass · fixed in Directus 12.0.0
- CVE-2026-42591 — Gotenberg SSRF in LibreOffice conversion · fixed in Gotenberg 8.32.0
hall of fame
- Nokia — Responsible Disclosure Hall of Fame, 2022
- NVIDIA — Product Security Acknowledgement, 2023
- Texas — Hall of Fame, 2022
- University of Twente — Hall of Fame, 2026
- Proofpoint — Security Recognition, 2026
- Odoo — Hall of Fame, 2022
- Achmea — Responsible Disclosure Recognition, 2023 and 2025