2026-10-14 · writeup
IDOR in a billing API led to full invoice exposure
How changing one numeric ID exposed other customers’ invoices, and how the fix was verified.
Summary
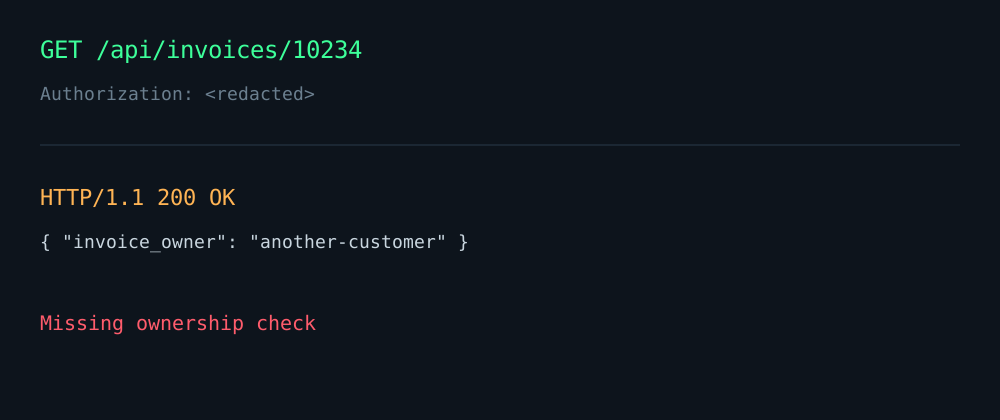
Changing one numeric invoice ID exposed another customer’s invoice because the API did not verify ownership.
Steps to reproduce
- Create or use an account with permission to view an invoice.
- Change the invoice identifier in the request.
- Confirm that a different customer’s invoice is returned.
Redact tokens and customer data from published evidence.
Impact and fix
An attacker could read other customers’ invoices. The fix must enforce authorization against the authenticated account on every invoice lookup.